Field notes
Investigations and case write-ups.
What real intrusions look like, and how they come apart once you start pulling on them. Written for people who want the technical details left in.
When the EDR runs out of road: memory forensics for 400 SOC analysts
On 21 October we taught memory forensics at the Comunidad DOJO SOC Level 2 bootcamp. The case we walked through: a process-injection alert where the EDR could prove something was injected, but not what.
 Sep 2026
INC Ransom in Panama: how the group behind the Metales Panamericanos attack operates
The INC Ransom gang listed Metales Panamericanos on its leak site. How the group operates, and what a Panamanian SMB can do to cut its risk.
 Jul 2026
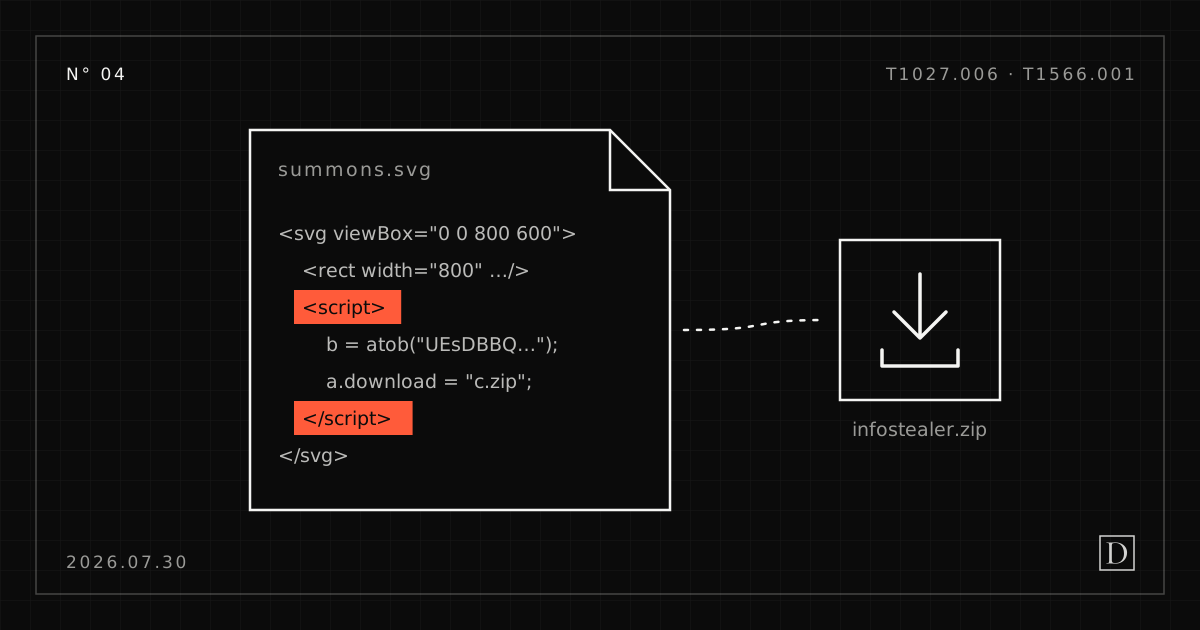
SVG smuggling: an infostealer disguised as a court summons
An .svg file with embedded JavaScript kicked off a social-engineering chain ending in a downloaded infostealer. No macro, no exploit, just a file type nobody expects to run code.
 Jul 2026
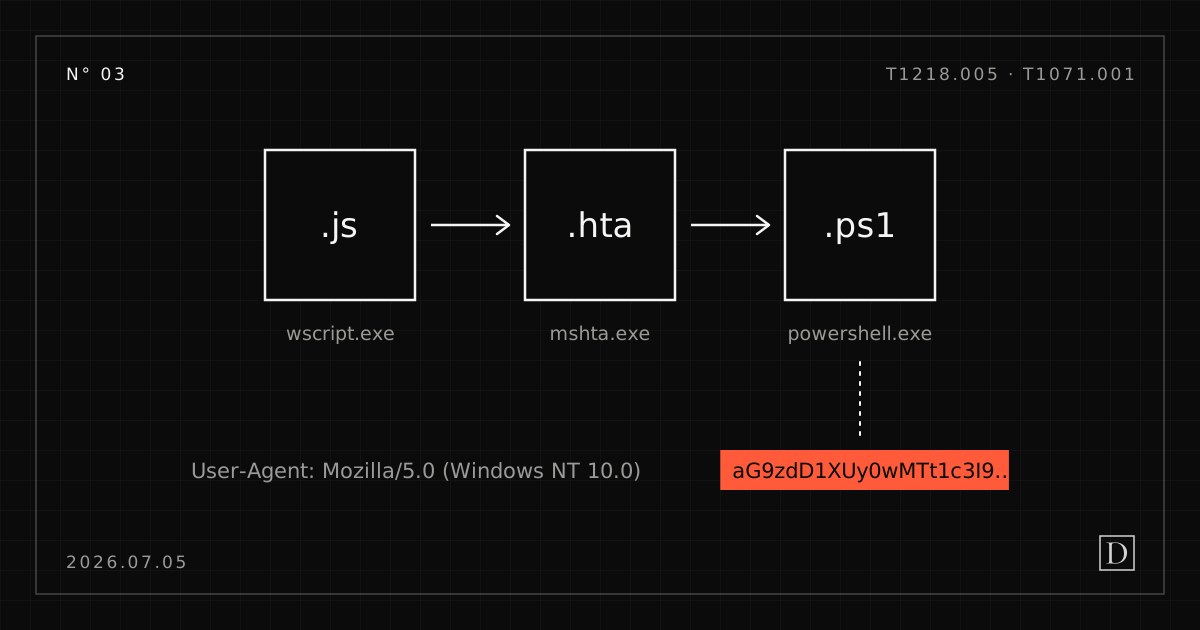
Vibecoded RAT? A LOLBins chain hiding behind an HTA file
A phishing lure impersonating Colombian authorities chained three legitimate Windows binaries to deploy a Remote Access Trojan (RAT) that hid its C2 traffic in the User-Agent header.
 Jun 2026
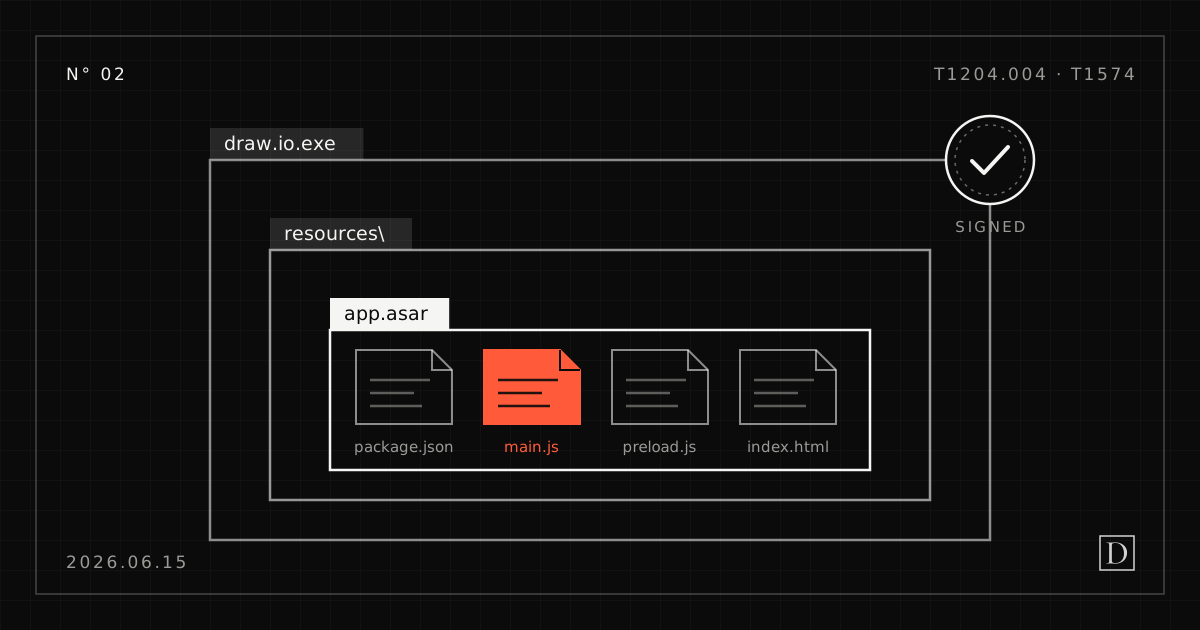
Anatomy of a ClickFix-to-RAT campaign: trojanizing Electron's app.asar
A signed binary, clean DLLs, and one tampered app.asar archive: how a fepafut[.]com ClickFix lure led to a persistent RAT that inherited draw.io's trust chain.
 Jun 2026
Sweeping common persistence, fast
The handful of registry keys, scheduled tasks, and services that account for most real-world persistence, and how to triage them in minutes.